THREAT INTELLIGENCE
Some WordPress sites can still be attacked while they install the fix for an actively exploited flaw, according to Umut Bayram, the Picus…
noviembre 6, 2026
LEER →
THREAT INTELLIGENCE
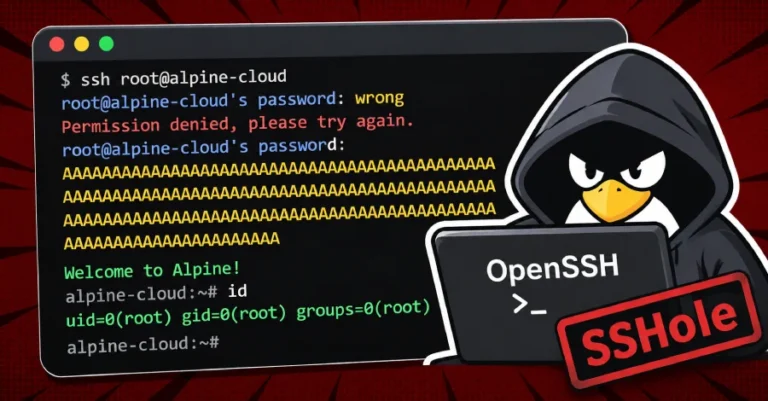
Threat actors are attempting to exploit a recently disclosed security flaw impacting OpenSSH that can enable sign-ins to accounts that have no password…
noviembre 6, 2026
LEER →
THREAT INTELLIGENCE
OpenAI on Thursday unveiled GPT‑6 Cyber, which it described as a major step forward in security research that brings together stronger cybersecurity capabilities…
noviembre 6, 2026
LEER →
THREAT INTELLIGENCE
A fix for CVE-2026-83844, a remote code execution flaw in Windows Paint, is now in the Microsoft Store. Paint gets this fix only…
noviembre 6, 2026
LEER →
THREAT INTELLIGENCE
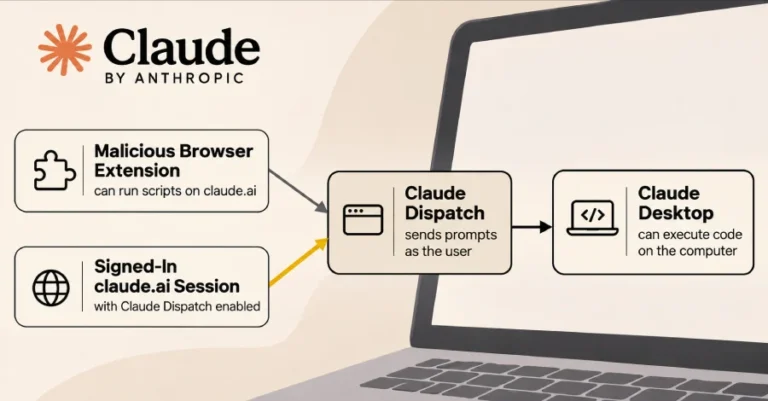
A browser extension that can run scripts on claude.ai could make Claude Desktop run code on a person's computer, researchers at Forever Security,…
noviembre 6, 2026
LEER →
THREAT INTELLIGENCE
An update on Athena, and some unsolicited predictions on what's coming next On Saturday, Dario Amodei published We Must Pace the Frontier. I…
noviembre 6, 2026
LEER →
THREAT INTELLIGENCE
Blockchain analysis firm Chainalysis has revealed that its ongoing investigation into the agentic cyber attack targeting its systems also exposed names, usernames, password…
noviembre 6, 2026
LEER →
THREAT INTELLIGENCE
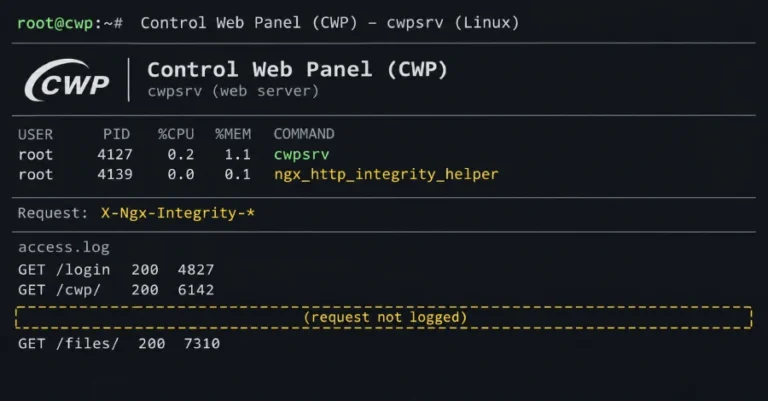
A backdoor has been found hiding in the web server that runs Control Web Panel (CWP), a free panel for managing Linux hosting…
noviembre 6, 2026
LEER →
THREAT INTELLIGENCE
Two flaws in Barracuda's Email Security Gateway, an email-filtering appliance, can be chained to run commands on it as root, its highest level…
noviembre 6, 2026
LEER →
THREAT INTELLIGENCE
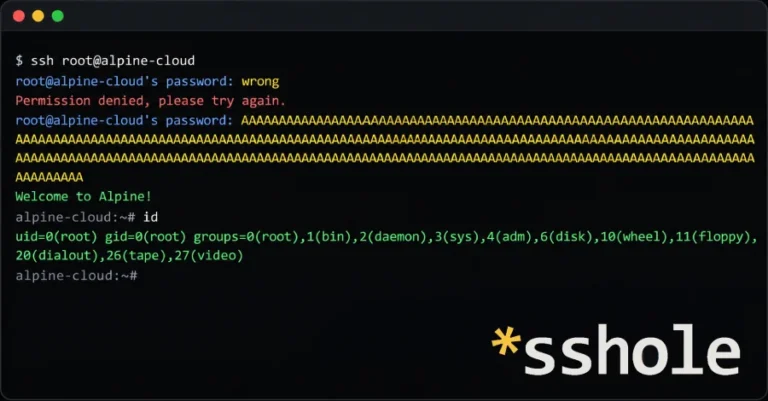
Attackers can log in to accounts that have no password, such as SSH key-only accounts, on some Alpine Linux servers running the standard…
noviembre 5, 2026
LEER →