THREAT INTELLIGENCE
An attacker tried to exploit a critical GitLab vulnerability on the Alpine Linux project's own GitLab server a week after GitLab released a fix,…
octubre 29, 2026
LEER →
THREAT INTELLIGENCE
Hackers exploited a critical Cisco Catalyst SD-WAN flaw, fixed in February, to plant custom malware inside the systems that control an organization's SD-WAN…
octubre 29, 2026
LEER →
THREAT INTELLIGENCE
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added a security flaw impacting Broadcom VMware ESX to its Known Exploited Vulnerabilities…
octubre 29, 2026
LEER →
THREAT INTELLIGENCE
Palo Alto Networks on Wednesday warned that threat actors are exploiting the recently patched PHP2Shell vulnerabilities against publicly-accessible management interfaces. "Active exploitation has…
octubre 29, 2026
LEER →
THREAT INTELLIGENCE
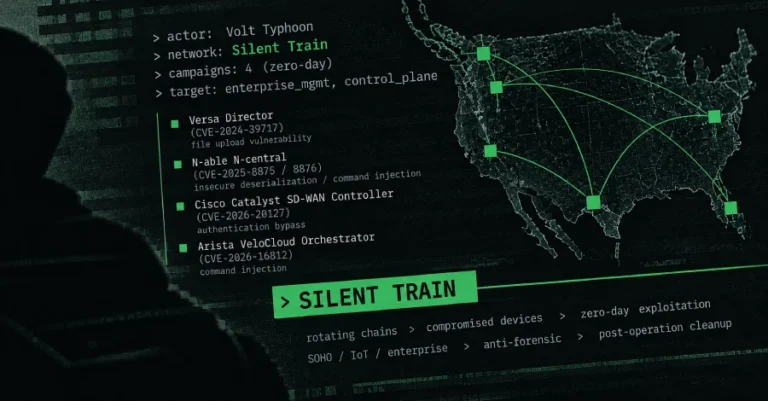
The China-nexus cyber espionage group known as Volt Typhoon has been attributed to a now-disrupted covert access network dubbed Silent Train that has…
octubre 28, 2026
LEER →
THREAT INTELLIGENCE
Third-party Android app stores can now apply to Google for permission to install apps with one tap, without Android's usual confirmation screens, and…
octubre 28, 2026
LEER →
THREAT INTELLIGENCE
A chain of logic flaws, with no memory corruption, can turn a malicious web page into code running on a Windows computer outside…
octubre 28, 2026
LEER →
THREAT INTELLIGENCE
Cybersecurity researchers have disclosed details of what appears to be an artificial intelligence (AI)-assisted attack orchestrated by a suspected China-nexus threat actor that…
octubre 28, 2026
LEER →
THREAT INTELLIGENCE
Threat actors are beginning to probe for a newly patched critical vulnerability in Oracle E-Business Suite (EBS), according to threat intelligence firm Defused…
octubre 28, 2026
LEER →
THREAT INTELLIGENCE
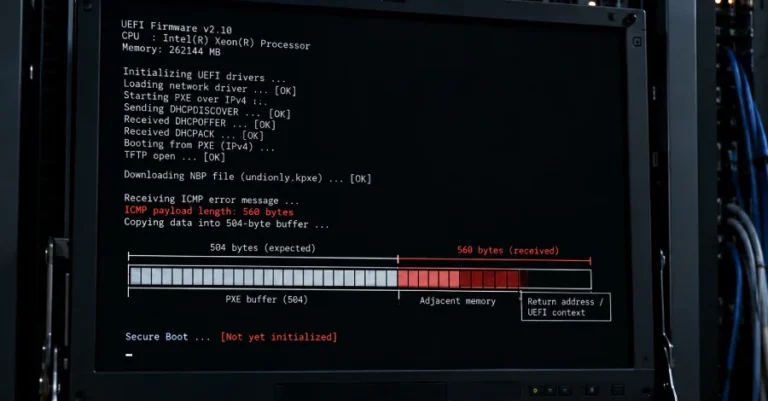
A critical 16-year-old flaw in EDK II, the open-source code that most hardware makers use to build UEFI firmware, can allow an attacker…
octubre 28, 2026
LEER →