GoAhead TLS Flaws Allow Revoked Client Certificates and Enable Session Decryption
The GoAhead embedded web server loaded a certificate revocation list into its default TLS backend but never turned revocation checking on, so a…
LEER →
The GoAhead embedded web server loaded a certificate revocation list into its default TLS backend but never turned revocation checking on, so a…
LEER →
Apple on Monday backported fixes for a high-severity security flaw that was exploited in real-world cyber attacks to older devices. The vulnerability, tracked…
LEER →
Microsoft has fixed a flaw in its Authenticator app for Android that let a malicious app with no permissions pose as a trusted…
LEER →
An attacker who gained access to Keystone's website obtained the key that its hardware wallets use to prove they are genuine, the company…
LEER →
Fake login pages are nothing new, but generative AI is making them easier to build and more convincing. Attackers can recreate familiar login…
LEER →
The North Korea-linked Lazarus Group has been attributed to a cyber espionage campaign dubbed Operation FlashHole targeting at least three organizations in South…
LEER →
A criminal using the Amadey malware can no longer access or steal data from 180,000 infected computers around the world, including some in…
LEER →
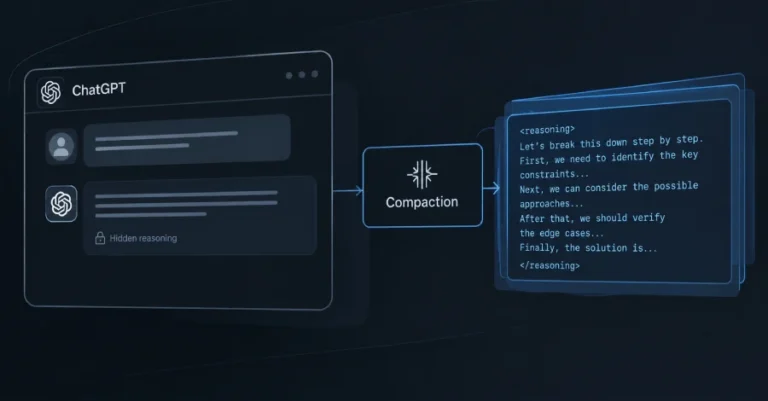
OpenAI's compaction feature, which shrinks a long conversation to save space, could be turned into a way to copy a model's hidden reasoning…
LEER →
The Computer Emergency Response Team of Ukraine (CERT-UA) has issued an alert warning of unauthorized remote access to video surveillance systems manufactured by…
LEER →
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Monday confirmed active exploitation of the recently patched PHP2Shell flaws by adding them to…
LEER →