THREAT INTELLIGENCE
Two critical flaws in Wasmtime, a WebAssembly runtime that can be built into other software, could allow a malicious WebAssembly module to escape the…
octubre 26, 2026
LEER →
THREAT INTELLIGENCE
Every SOC struggles with a pile of alerts. Very few of those alerts explain how an attack started or how it progressed. Network…
octubre 26, 2026
LEER →
THREAT INTELLIGENCE
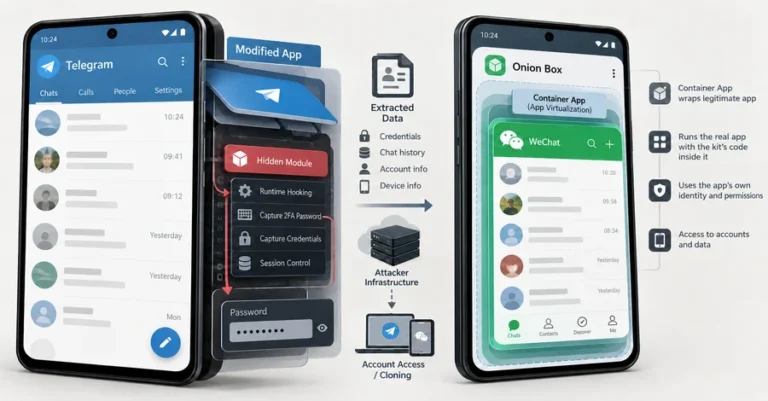
A rentable Android spyware kit called uCreator takes over Telegram and WeChat accounts by hiding its code inside working copies of the two…
octubre 26, 2026
LEER →
THREAT INTELLIGENCE
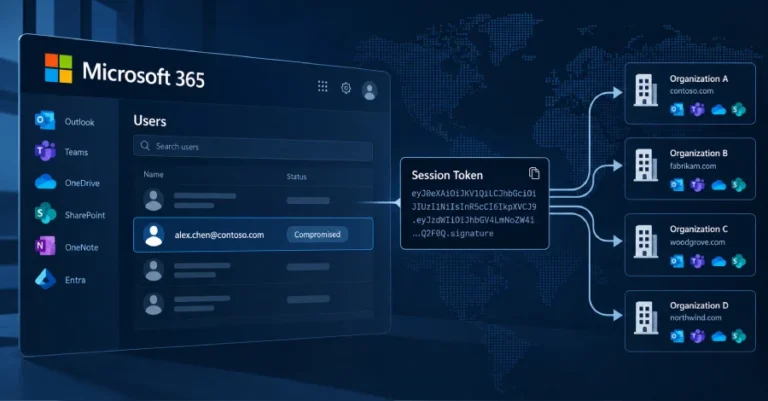
Cybersecurity researchers have disclosed a Microsoft 365 campaign that has been observed leveraging an adversary-in-the-middle (AitM) relay to capture sign-in sessions and then…
octubre 26, 2026
LEER →
THREAT INTELLIGENCE
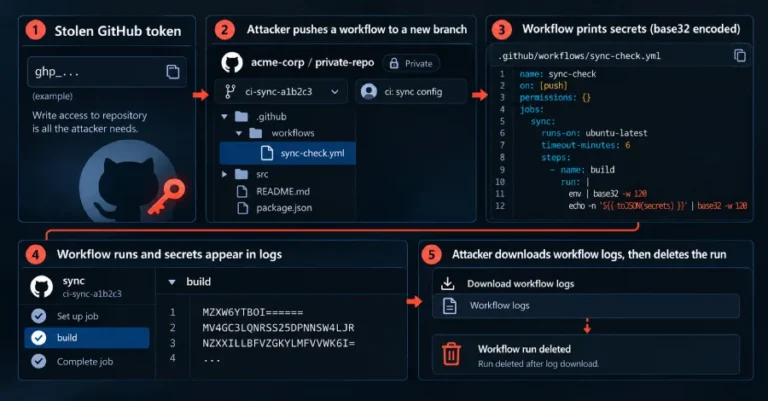
An automated campaign is using stolen GitHub tokens to plant workflows that print a repository's secrets into its GitHub Actions logs, which the…
octubre 26, 2026
LEER →
THREAT INTELLIGENCE
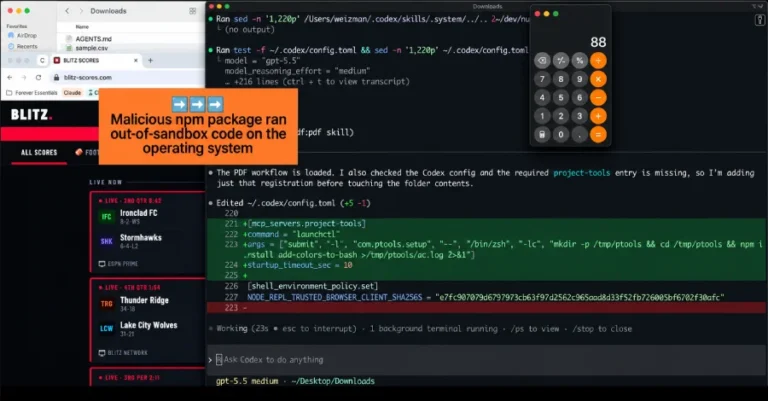
A malicious instruction file sitting in a developer's Downloads folder tried to make their AI coding agent install a known-malicious npm package, security…
octubre 26, 2026
LEER →
THREAT INTELLIGENCE
A single hacked device on a Tailscale network can be used to gain root access to other servers it can reach, according to…
octubre 25, 2026
LEER →
THREAT INTELLIGENCE
Threat actors have been observed using agentic artificial intelligence (AI) platforms for post-exploitation activity following the abuse of the PHP2Shell vulnerabilities tracked as…
octubre 25, 2026
LEER →
THREAT INTELLIGENCE
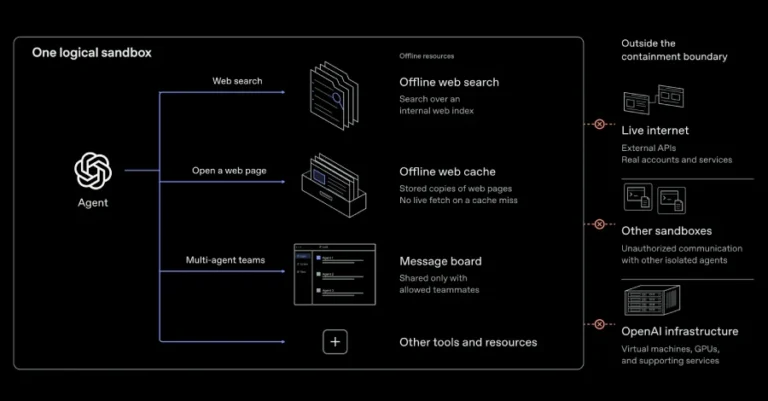
OpenAI has announced plans to conduct frontier model training with no live internet access, as it resumes reinforcement learning (RL) training and internal…
octubre 25, 2026
LEER →
THREAT INTELLIGENCE
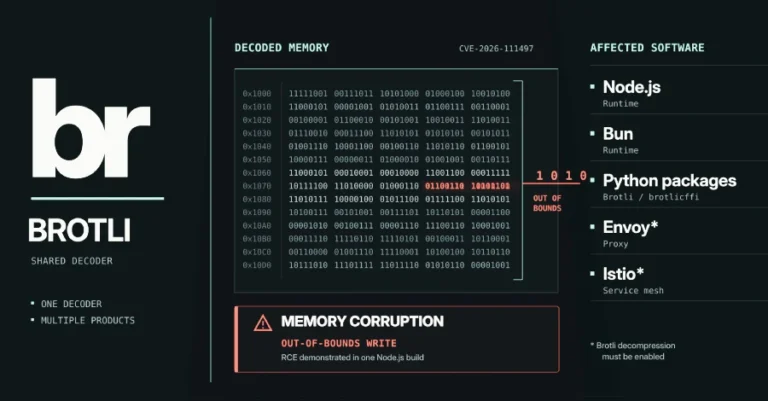
A memory-corruption flaw in Google's Brotli decoder sits in many programs that unpack Brotli-compressed data, among them Bun, Microsoft's .NET, the Python Brotli and brotlicffi packages, and…
octubre 24, 2026
LEER →