THREAT INTELLIGENCE
Pillow, the most widely used image library for Python, can be made to run operating system commands on a server by specifying the…
octubre 23, 2026
LEER →
THREAT INTELLIGENCE
Malicious Brotli data can make an application on an official build of Node.js run attacker-supplied code, security researchers at Imperva have demonstrated. Their "Node2Shell"…
octubre 23, 2026
LEER →
THREAT INTELLIGENCE
AI agents paying for API calls with the x402 SDKs could sign a payment for their full balance of a supported token if a malicious…
octubre 23, 2026
LEER →
THREAT INTELLIGENCE
Threat actors have been observed unsuccessfully attempting to exploit the newly disclosed PHP2Shell vulnerabilities to rope infected systems into a Mirai botnet variant…
octubre 23, 2026
LEER →
THREAT INTELLIGENCE
Right now, there is probably an AI agent running on a laptop somewhere in your network. It stores API keys and database passwords,…
octubre 22, 2026
LEER →
THREAT INTELLIGENCE
Attackers are exploiting a zero-day SQL injection flaw in Arista's VeloCloud Orchestrator (VCO), the central management system for VeloCloud SD-WAN networks, the company said in…
octubre 22, 2026
LEER →
THREAT INTELLIGENCE
eMudhra, an Indian certificate authority (CA), will withdraw from its global SSL/TLS certificate business, its board decided on Thursday. The decision came five days…
octubre 22, 2026
LEER →
THREAT INTELLIGENCE
This week has already been rough for cybersecurity. Critical PHP and GitLab RCE flaws, serious Linux security bugs, compromised eMudhra certificates, a Node.js…
octubre 22, 2026
LEER →
THREAT INTELLIGENCE
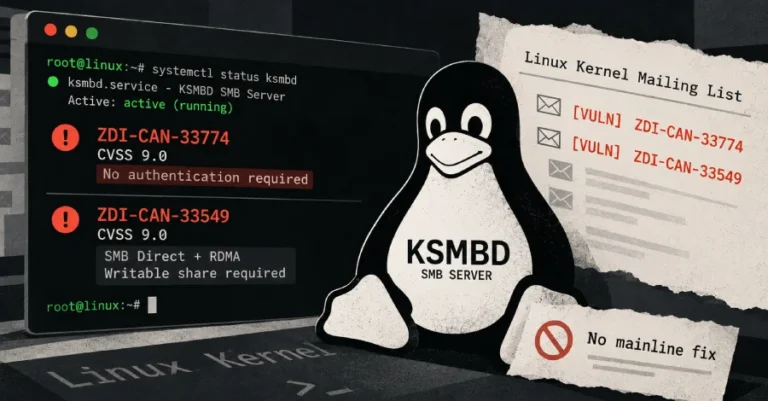
Linux servers running KSMBD, the kernel's built-in SMB server, are exposed to two publicly reported remote code execution flaws rated 9.0 by Trend Micro's…
octubre 22, 2026
LEER →
THREAT INTELLIGENCE
Social media giant Meta was ordered to pay 25 billion in penalties by a New Mexico court on Wednesday as part of a…
octubre 22, 2026
LEER →