THREAT INTELLIGENCE
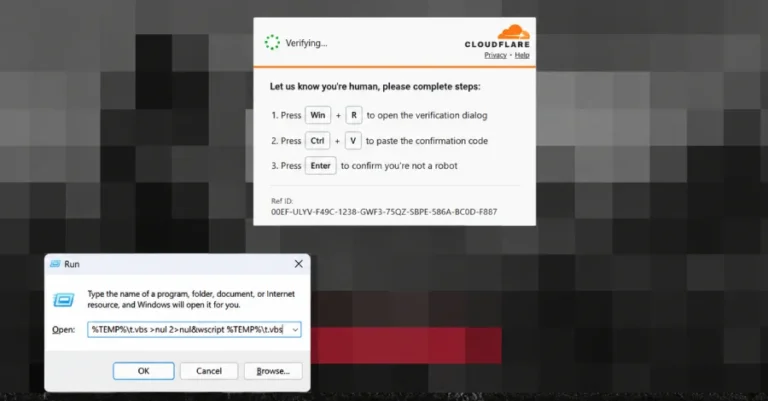
ClickFix Smuggles Payloads Through Browser Cache to Bypass Windows Run Limits
A new type of ClickFix attack is using compromised websites to trick users into executing a malicious payload cached in a web browser's…
LEER →A new type of ClickFix attack is using compromised websites to trick users into executing a malicious payload cached in a web browser's…
LEER →
Microsoft has released out-of-band security updates to address a high-severity flaw in Microsoft Exchange Server that could allow an attacker to escalate privileges…
LEER →
A blank field. A public repo. One reply to an email. A box left exposed. None of this sounds dramatic, which is partly…
LEER →
Every modern enterprise depends on credentials. This is how humans, systems, and now AI, all connect to data, services, and each other securely.…
LEER →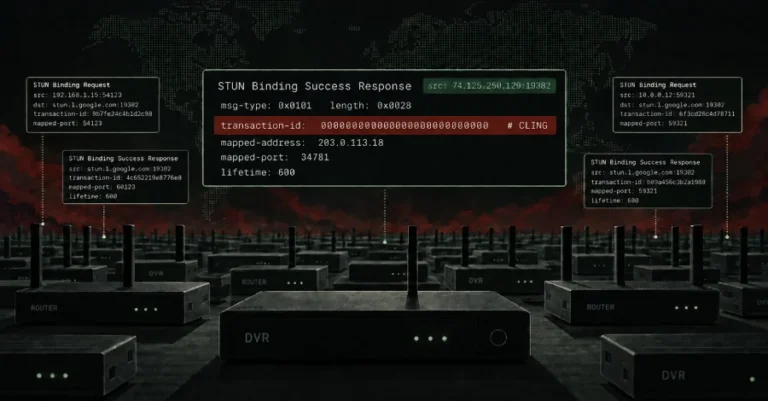
Threat actors have been observed attempting to exploit a now-patched critical security flaw impacting the Realtek Jungle software development kit (SDK) to deploy…
LEER →
Apple has announced that it's taking steps to tighten controls around a macOS setting called Full Disk Access (FDA) due to security risks…
LEER →
A critical security flaw impacting Rejetto HTTP File Server (HFS) is witnessing active exploitation attempts, according to VulnCheck. The vulnerability in question is…
LEER →
Citrix has released security updates for a high-severity security flaw in NetScaler ADC and Citrix NetScaler Gateway that has been exploited as part…
LEER →
A suspected member of the ShinyHunters digital extortion group, who goes by the online alias "Rey," has been allegedly detained by authorities in…
LEER →
A new China-nexus cyber espionage group known as TA419 has been attributed to multiple credential phishing campaigns targeting artificial intelligence (AI) experts working…
LEER →